If you found 13.232.238.236 in a server log, firewall report, analytics record, or network scan, current network data provides useful information about the address. It is associated with Amazon Web Services infrastructure in India, routed through AS16509, Amazon.com, Inc., and has the reverse-DNS hostname ec2-13-232-238-236.ap-south-1.compute.amazonaws.com.
The ap-south-1 portion of the hostname corresponds to AWS’s Asia Pacific (Mumbai) region. However, public IP data does not reveal the specific AWS customer, application, or individual using the address at a particular time.
| Quick Fact | Details |
|---|---|
| IP Address | 13.232.238.236 |
| IP Version | IPv4 |
| ASN | AS16509 |
| ASN Organization | Amazon.com, Inc. |
| Associated Company | Amazon Data Services India |
| Network Name | AMAZON-BOM |
| BGP / Network Prefix | 13.232.0.0/14 |
| Reverse DNS | ec2-13-232-238-236.ap-south-1.compute.amazonaws.com |
| Cloud Provider | Amazon Web Services / Amazon EC2 |
| AWS Region | Asia Pacific (Mumbai), ap-south-1 |
| Approximate Geolocation | Mumbai City, Maharashtra, India |
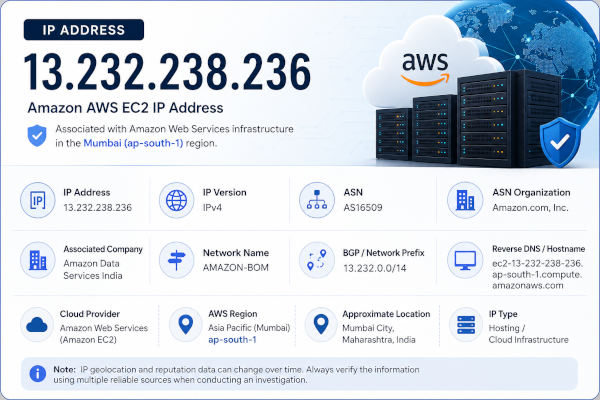
These details reflect current public network, routing, and geolocation data. Some information associated with cloud infrastructure can change over time.
What is 13.232.238.236?
13.232.238.236 is a public IPv4 address associated with Amazon Web Services infrastructure. Its network is announced through AS16509, an autonomous system operated by Amazon.com, Inc.
Its reverse-DNS hostname is:
ec2-13-232-238-236.ap-south-1.compute.amazonaws.com
The hostname is consistent with Amazon EC2 infrastructure and also identifies the AWS region associated with the address.
This provides useful information about the network behind the IP, but it does not identify the exact workload running on it. AWS infrastructure is used by many different customers and applications, so the network owner should not be confused with the organization or person responsible for a particular request.
Who Owns 13.232.238.236?
At the routing level, 13.232.238.236 is associated with AS16509, Amazon.com, Inc. Current network information also associates this address range with Amazon Data Services India and the network name AMAZON-BOM.
The broader network prefix associated with the IP is:
13.232.0.0/14
You can also check the official AWS IP address ranges to verify whether an IP block is associated with Amazon Web Services.
This range covers addresses from:
13.232.0.0 to 13.235.255.255
Amazon operates the network, but an individual address within that network may be assigned to an AWS resource used by a customer.
Public ASN, WHOIS, or RDAP information does not reveal which AWS account was responsible for a specific request reaching your website or server.
13.232.238.236 Hostname and AWS Region
The current reverse-DNS hostname for 13.232.238.236 is:
ec2-13-232-238-236.ap-south-1.compute.amazonaws.com
There are two useful parts of this hostname.
ec2 is associated with Amazon Elastic Compute Cloud, while ap-south-1 is the AWS region code for the Asia Pacific (Mumbai) region.
This makes the hostname particularly useful when investigating the address because it provides both cloud-platform context and the associated AWS region.
The region should not be interpreted as the physical location of the person or organization using the resource. A customer can operate an AWS resource in Mumbai while being located elsewhere.
Network and IP Range Details
When researching 13.232.238.236, you may encounter more than one network range.
The address falls within:
13.232.238.0/24
A /24 contains 256 IPv4 addresses, ranging from 13.232.238.0 through 13.232.238.255. Looking at this smaller block can be useful when checking nearby addresses or related reverse-DNS patterns.
The broader network associated with the address is:
13.232.0.0/14
This range provides more useful context for network ownership and routing and is associated with AS16509.
In practical terms, the /24 is useful for examining nearby IP addresses, while the /14 provides the broader network and BGP context.
Why Might 13.232.238.236 Appear in Your Server Logs?
If 13.232.238.236 appears in an access log, firewall event, authentication log, or security report, the connection involves an IP associated with AWS infrastructure.
That fact alone does not explain why the request occurred.
AWS infrastructure can run many different customer workloads, so identifying Amazon as the network operator does not identify the application that generated the traffic.
To understand what happened, examine the information recorded by your server, including:
- the URL or endpoint requested;
- HTTP method and response status;
- exact timestamp;
- frequency of requests;
- user-agent string;
- authentication attempts;
- unusual request headers;
- requests for sensitive or nonexistent paths;
- related activity from other IP addresses.
A single request to a normal public page should be evaluated differently from hundreds of failed login attempts or rapid requests across sensitive endpoints.
The behavior of the traffic provides more useful security information than the identity of the cloud provider alone.
Is 13.232.238.236 Safe or Dangerous?
There is no reliable basis for calling 13.232.238.236 dangerous simply because it is associated with AWS.
At the time this address was researched, the security data checked did not classify it as a known attacker, Tor exit node, VPN, proxy, spam source, or bot. It was identified as cloud-provider infrastructure.
However, IP reputation can change.
Cloud addresses may be assigned to different resources or workloads over time, and security databases can update their classifications when new activity is detected.
A clean reputation result therefore does not guarantee that every request from an IP is harmless. Similarly, unfamiliar traffic should not automatically be treated as malicious.
If you are investigating the address because of activity on your own website, the strongest evidence will usually come from your server logs.
Can 13.232.238.236 Reveal Someone’s Exact Location?
No.
Current geolocation data associates 13.232.238.236 with Mumbai, Maharashtra, India, which is consistent with the ap-south-1 AWS region shown in its hostname.
That does not mean the person or organization using the IP is physically located in Mumbai.
With cloud infrastructure, IP geolocation generally provides information about the network or data-center region rather than the exact location of the customer operating a resource.
An IP lookup cannot normally reveal someone’s home address, exact physical location, personal identity, or the identity of an AWS account holder.
Should You Block 13.232.238.236?
Do not block 13.232.238.236 solely because you do not recognize the address.
If the requests are normal, blocking the IP may be unnecessary. If your logs show abusive behavior such as repeated authentication failures, aggressive scanning, exploit attempts, or excessive request volume, taking action may be appropriate.
Depending on the activity, possible responses include:
- rate limiting;
- firewall rules;
- login protection;
- bot controls;
- WAF rules;
- temporary IP blocking;
- additional log analysis.
A targeted response is generally better than blocking a large network without evidence.
In particular, avoid blocking the entire 13.232.0.0/14 network unless you have a strong operational reason. The range contains many IP addresses and may include unrelated AWS workloads.
How to Investigate 13.232.238.236
If you need to investigate activity from 13.232.238.236, start with the exact timestamp recorded in your logs.
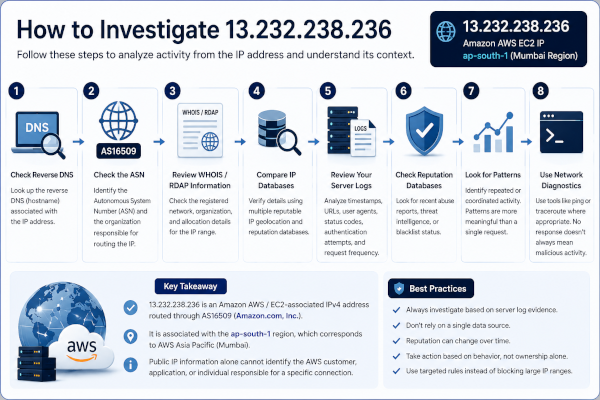
Time matters when dealing with cloud infrastructure because public IPv4 addresses can be reassigned or associated with different resources over time.
A practical investigation process includes:
- Check reverse DNS – Confirm the current hostname associated with the address.
- Check the ASN – Identify the organization responsible for routing the IP.
- Review RDAP or WHOIS information – Confirm the registered network and its associated organization.
- Compare multiple IP databases – Avoid relying on a single geolocation or reputation service.
- Review your server logs – Examine requested URLs, timestamps, user agents, status codes, authentication activity, and request frequency.
- Check current reputation databases – Look for recent abuse or threat-intelligence reports if the traffic appears suspicious.
- Look for patterns – Repeated or coordinated activity usually provides more useful evidence than a single isolated request.
- Use network diagnostics where appropriate – Tools such as ping or traceroute may provide additional network information, although a host that does not respond is not necessarily offline or malicious.
Based on current public information, the clearest conclusion is that 13.232.238.236 is an Amazon AWS/EC2-associated IPv4 address routed through AS16509 and associated with AWS’s Asia Pacific (Mumbai) region.
Public IP information alone cannot identify the AWS customer, application, or individual responsible for a specific connection.
Frequently Asked Questions
Is 13.232.238.236 an AWS IP address?
Yes. 13.232.238.236 is associated with AS16509, Amazon.com, Inc., and its reverse-DNS hostname is consistent with Amazon EC2 infrastructure in the ap-south-1 AWS region.
Where is 13.232.238.236 located?
Current network and geolocation information associates it with Mumbai, Maharashtra, India. AWS identifies ap-south-1 as its Asia Pacific (Mumbai) region.
This does not reveal the physical location of the customer using the IP.
Who owns 13.232.238.236?
The address is routed through AS16509, Amazon.com, Inc. Current network information also associates the relevant range with Amazon Data Services India and the network name AMAZON-BOM.
What is the hostname of 13.232.238.236?
The current reverse-DNS hostname is:
ec2-13-232-238-236.ap-south-1.compute.amazonaws.com
The hostname is consistent with Amazon EC2 infrastructure in AWS’s Mumbai region.
Is 13.232.238.236 malicious?
There is currently not enough evidence to label 13.232.238.236 malicious based solely on public IP information.
If the IP appears in your logs, evaluate its request behavior and check current reputation data before deciding whether it should be blocked.
Why is 13.232.238.236 connecting to my website?
Public IP information cannot reveal the exact application using the address.
Check the requested URLs, timestamps, user agent, request frequency, authentication attempts, status codes, and other server-log information to determine what the traffic was doing.
Can 13.232.238.236 identify a specific person?
No. Public IP records can identify the network provider and approximate infrastructure region, but they do not reveal the individual or AWS customer responsible for a particular connection.

